TRENDING

Saturday, 14 November 2026
----------------------
4 Jumada Al-Thani 1448 AH
Germany has granted its intelligence services sweeping authority to hack and disrupt perceived threats. The move promises stronger defense but raises fresh concerns over privacy and state overreach.
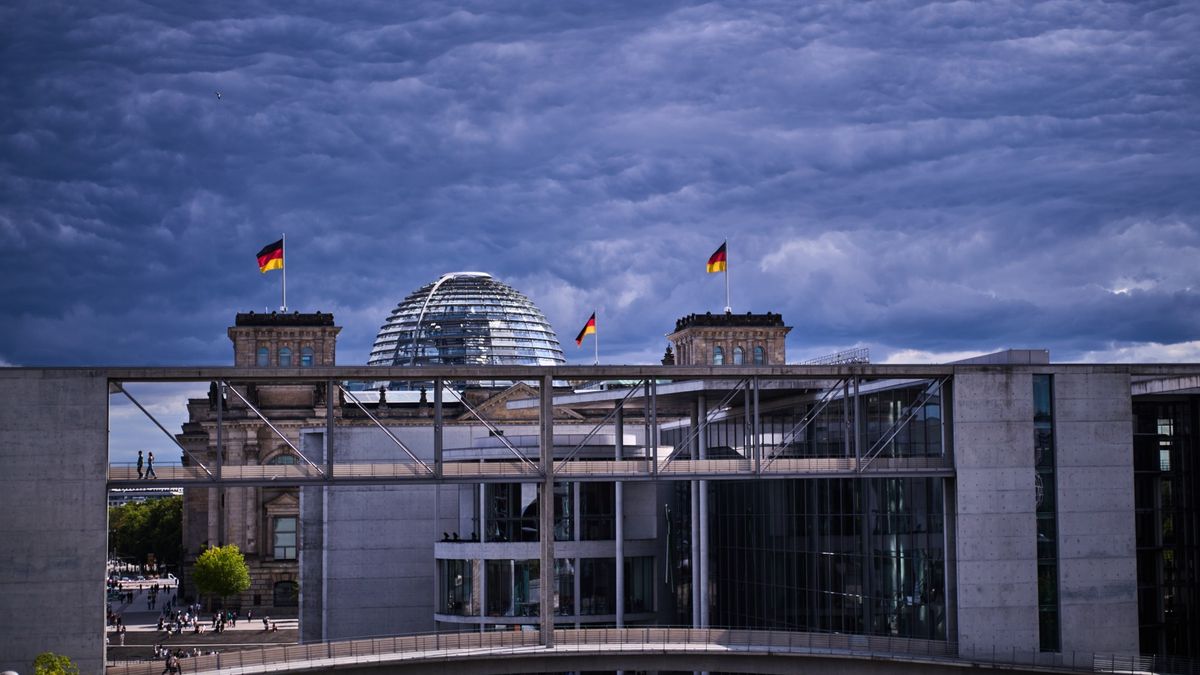
Germany’s parliament voted on 14 November 2026 to give the Bundesnachrichtendienst (BND) and the Federal Office for the Protection of the Constitution (BfV) the legal right to conduct offensive cyber operations. The bill passed 308‑190 with 71 abstentions, backed by the governing Christian Democrats and Social Democrats, while the far‑right AfD and the left‑wing Die Linke opposed it. Under the new framework the agencies can delete stolen data from hostile servers, jam foreign hacking infrastructure, and intervene when no other authority can act. The reforms are slated to take effect on 31 December after final legislative steps.
The legislation is a response to a perceived gap in Germany’s security architecture. Alexander Dobrindt, the interior minister, framed it as a “reform of the century,” arguing that without offensive tools the country is forced to watch threats unfold. Politically, the governing coalition needed a tangible win ahead of the upcoming state elections, especially in Berlin where Die Linke has just secured a mayoral position. By positioning the bill as a defensive necessity, the coalition sidesteps criticism of being soft on Russia after the Leipzig‑Halle drone incident, while also signaling to NATO allies that Berlin can shoulder a larger share of the cyber‑defence burden.
Strategically, the move aligns Germany with other Western intelligence services that already possess similar powers, such as the United Kingdom’s GCHQ and the United States’ NSA. The promise of “equal footing” is meant to reassure partners that Germany will not be a weak link in the alliance’s collective cyber‑deterrence. At the same time, the law creates a new bureaucratic arena where the BND and BfV can bypass traditional police channels, consolidating power within the intelligence community and reducing parliamentary oversight.
The most immediate victims are ordinary Germans whose online activities may now be subject to covert intrusion. Civil‑rights groups warn that the expanded remit blurs the line between intelligence gathering and police enforcement, echoing the surveillance practices of the Stasi in former East Germany. For citizens who grew up under that regime, the prospect of a modern secret police evokes deep mistrust and fear.
Small‑ and medium‑sized businesses are also at risk. Companies that handle sensitive data—particularly in the tech and manufacturing sectors—could become collateral targets if their networks are used as launch pads for foreign hackers. The law gives the BND permission to disrupt foreign servers, but the technical means to do so often involve infiltrating domestic infrastructure first, exposing private firms to legal and reputational fallout.
Finally, the diaspora communities linked to Russia, Ukraine, and the Middle East may face heightened scrutiny. Past incidents show that intelligence services sometimes use broad threat definitions to monitor ethnic or political groups, leading to a chilling effect on free expression and community organizing.
Official statements stress that the powers are limited to “serious threats” and require parliamentary approval for each operation. In practice, the criteria for what counts as serious remain vague, giving the agencies wide discretion. What is omitted is the growing dependence on private tech firms for cyber‑tools. Companies that develop zero‑day exploits or provide cloud‑based surveillance platforms stand to profit from a state that now has a legal mandate to purchase and deploy such capabilities.
Another blind spot is the deteriorating intelligence sharing with the United States. German officials have cited “US unpredictability” as a catalyst for the reform, yet they rarely acknowledge that tighter domestic controls could complicate joint operations, especially when American agencies demand reciprocal access to German data streams. This tension may push Berlin to develop more autonomous capabilities, further insulating the intelligence community from external oversight.
Lastly, the narrative downplays the retaliatory calculus of Russia. The Leipzig‑Halle drone episode already prompted a diplomatic tit‑for‑tat, with consulates closing on both sides. By granting offensive cyber tools, Germany risks escalating a covert cyber‑war that could spill over into civilian infrastructure, a scenario that officials are keen to keep out of public debate.
Watch for the first operational orders issued under the new law, especially any that target foreign servers linked to Russian state‑backed groups. Parliamentary committees will soon be tasked with reviewing the law’s implementation; the depth and transparency of those hearings will indicate whether oversight mechanisms can keep pace with the expanded powers. Keep an eye on court challenges brought by privacy NGOs, as successful litigation could force the government to narrow the scope of the authority. Finally, monitor how NATO and EU partners respond—whether they welcome Germany’s new capabilities or raise concerns about escalation—because the balance of cyber‑deterrence in Europe may shift dramatically in the coming months.
The BND and BfV can now conduct offensive cyber actions, such as deleting stolen data from attackers' servers and disrupting foreign hacking infrastructure, when a serious threat is identified.
The broader remit blurs the line between intelligence work and police surveillance, raising privacy concerns and reviving fears of state overreach reminiscent of the Stasi era.
Editor's Note: Analysis based on publicly available legislative texts and expert commentary; operational details remain classified.
Source referenced: ALJAZEERA
This brief was synthesized by our Editorial Engine and reviewed by The Ground Narrative team.